Knowledge Base / Security Advisories
October 27, 2026
Impacted Devices and Firmware:
Summary:
The PHP project recently disclosed two critical vulnerabilities in the PHP runtime that could allow an unauthenticated attacker to run code on a web server. Room Alert products do not use PHP and are not affected. As a precaution, AVTECH has patched AVTECH.com and RoomAlert.com. None of our systems were exploited.
Description:
On October 21, 2026, the PHP project released emergency updates to fix two critical vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619 and nicknamed “php2shell,” that allow an unauthenticated attacker to run code on servers running PHP. The vendor rates both CVSS 9.2. They affect any PHP installation that serves web requests, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. The fixed versions are PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12.
What This Means for You:
Not affected: Room Alert devices, software and local utilities.
Updated: our website and cloud portal.
Temporarily unavailable: Live Chat.
Recommendation:
No action is required for Room Alert devices, software or utilities. For any questions about this advisory, contact our support team at (401) 628-1600 or support@roomalert.com.


We'd love to talk with you about your monitoring needs. Contact one of our Product Specialists for a free consultation.

You may find Windows Command Prompt at the following path:
To run Windows Command Prompt as an administrator:
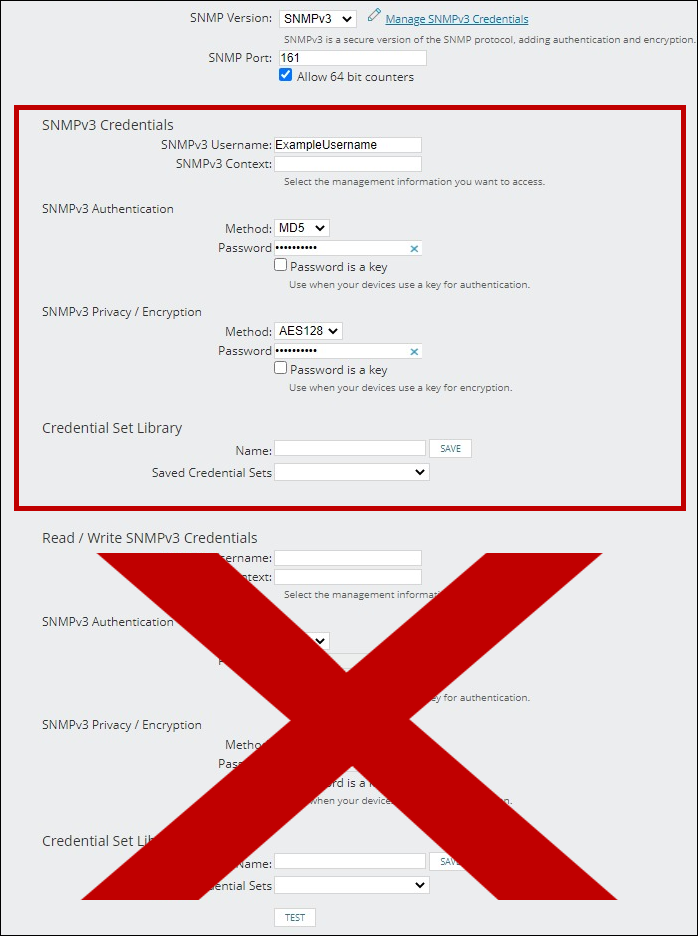
If you are using this client, you should configure the general SNMPv3 Credentials, but leave the Read / Write SNMPv3 Credentials section blank.

| Current S models | Current E models |
|---|---|
| Room Alert 32S | Room Alert 32E |
| Room Alert 12S | Room Alert 12E |
| Room Alert 3S | Room Alert 4E |
| Room Alert 3E | |
| S models | E & W models |
|---|---|
| Room Alert 32S | Room Alert 32E |
| Room Alert 12S | Room Alert 12E |
| Room Alert 3S | Room Alert 4E |
| Room Alert 3E | |
| Room Alert 3W |
| Model |
|---|
| Room Alert MAX |
| Room Alert 32S |
| Room Alert 12S |
| Room Alert 3S |
| Room Alert 32E/W |
| Room Alert 12E |
| Room Alert 4E |
| Room Alert 3E |
| Room Alert 3 Wi-Fi |